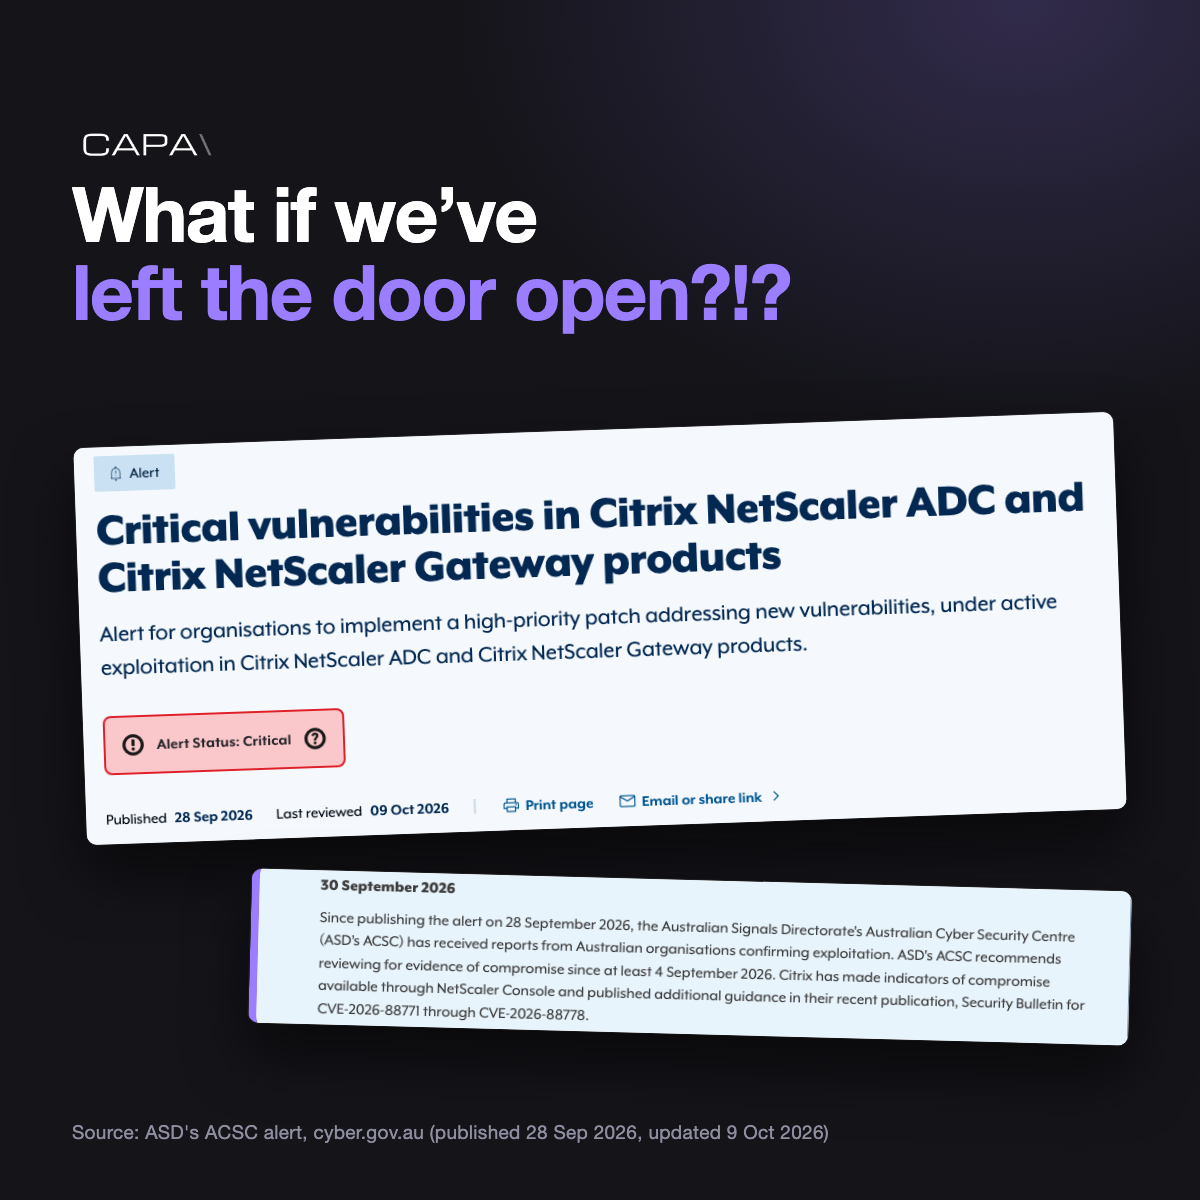
On 28 September 2026, the Australian Signals Directorate’s ACSC issued a critical alert on eight vulnerabilities in Citrix NetScaler ADC and Gateway, the appliances many organisations use to give staff and contractors remote access. At least two were being exploited around the world before a patch existed. Two days later, Australian organisations reported confirmed compromises, and ASD advised them to look for signs of intrusion going back to 4 September - the date when ASD published its previous critical NetScaler alert.
For energy operators, this isn’t a one-off. It’s the latest example of a pattern that has been with us for many years, but is now becoming more frequent. The appliances we put on the internet to let people in safely have become the most reliable way for attackers to gain access. Patching faster won’t change that on its own. The more useful question is what happens after an intruder gets through, and whether anyone notices before they reach the control systems.
Remote access is now the main way in
Dragos, the industrial OT cyber security firm, has reported in its 2026 Year in Review that 73% of its incident response cases involved active exploitation or credential reuse of VPNs or jump hosts. Half of its assessment engagements found weaknesses in secure remote access. The same pattern shows up in IT: Mandiant and Verizon both now rank exploitation of internet-facing systems, led by VPNs, firewalls and gateways, among the top ways attackers get in.
The energy sector has already seen the impacts. In December 2025, attackers struck more than 30 wind and solar farms and a heat and power plant in Poland. CERT Polska found that each affected substation had a FortiGate appliance acting as both firewall and VPN, exposed to the internet and accepting logins without multi-factor authentication. Once inside, the attackers used default passwords on substation controllers to load malicious firmware and wipe devices. Generation continued, but only because the sites were too small to matter to the national grid.
CERT Polska’s follow-up report, published in August 2026, showed how far one remote access path can reach. At one wind farm, the attacker used administrator rights on the FortiGate to obtain a VPN account with access to every network segment. From there, the attackers found a cellular router installed as a backup link, and moved laterally to a number of remote assets.
Poland isn’t an isolated case. Remote access has been a key pathway into energy systems for over a decade:
- Ukraine, December 2015. Attackers used stolen VPN credentials to reach the control systems of three distribution companies and opened breakers remotely, cutting power to about 225,000 customers.
- Germany, February 2022. A misconfigured VPN appliance let attackers into the management network of the KA-SAT satellite service. The attack, attributed to Russia, cut remote monitoring and control of about 5,800 Enercon wind turbines that relied on it.
- Denmark, May 2023. Attackers exploited a single flaw in Zyxel firewalls at 16 Danish energy companies at once and took control of the firewalls at 11. The flaw had been patched weeks earlier, and SektorCERT, the Danish energy sector’s CERT, noted that the attackers already knew which companies had vulnerable devices.
- Norway, April 2025. Pro-Russian hackers used a weak password on an internet-facing control panel to open a dam valve fully for about four hours.
- Ransomware, 2026. Dragos counted 12 ransomware incidents at renewable energy organisations worldwide in the second quarter of 2026 alone, with the leading groups getting in through VPN flaws and stolen VPN credentials.
And there’s more:
In October 2026, researchers at Modat and the Dutch National Cyber Security Centre found 8,547 internet-facing systems at wind farms and solar parks in 35 European countries, and estimated that full control would have been possible at about 181 sites. One turbine control page had Start, Stop and Reset buttons.
There is ample evidence to suggest that we have been “leaving the door open”, so to speak, for some time now.
The vendor track record
Every major remote access vendor has had serious exploited flaws in the past three years. Ivanti Connect Secure, Palo Alto GlobalProtect, Cisco’s ASA firewalls, SonicWall and Citrix (CitrixBleed in 2023, CitrixBleed 2 in 2025, and a run of exploited NetScaler flaws through 2026) have all appeared on the US government’s KEV list (list of known exploited vulnerabilities).
Fortinet deserves particular attention because FortiGate firewalls are so common in operational technology, especially at the small, unattended sites that make up most of the renewables fleet. Its SSL VPN has had repeated critical flaws exploited by state and criminal groups since 2022.
If that wasn’t enough, there were two further incidents involving previous patches that left gaps (the symlink persistence), and persistent malware that survived reboots and firmware upgrades.
The point here isn’t that Fortinet is uniquely bad. It’s that the whole category has a structural problem, and Fortinet’s significant footprint in OT makes the consequences more significant. Remote access appliances run large amounts of older code, offer services to anyone on the internet before they log in, and can’t run the endpoint detection tools that protect servers and laptops. Once they are compromised, the operator often has no way to see it, and patching can have mixed results as we have pointed to earlier.
The layered defences approach
Most mature energy operators don’t let remote users straight into OT. A typical design has a corporate log in through a corporate gateway such as Citrix, then users must connect to a jump host to log in separately to each site. That second layer is what typically stops a compromised gateway from automatically becoming an OT incident.
However, a compromised gateway can still put the attacker in a strong position. By way of example:
- Previous bugs in the CitrixBleed family leak session tokens, letting an attacker take over a logged-in user’s session and bypassing multi-factor authentication.
- Code execution on a gateway lets an attacker record every password typed at the login page and use them for further lateral movement.
- If the jump host is joined to the corporate directory, or OT permissions are managed through corporate groups, taking over the corporate network brings credentials into the OT properties.
So, when does the layered approach work, and when does it fail?
- At the Polish heat and power plant, the attacker tried twice, three days apart, to log into the plant’s own firewall using generic account names and one belonging to the telecontrol contractor. Both attempts failed, and they were reduced to scanning the network.
- At the Polish wind and solar farms, and at the 5,800 Enercon turbines cut off by the KA-SAT attack, generation continued. Turbines and inverters run safely without their communications link, so losing remote access didn’t mean losing the plant.
- In Denmark, SektorCERT’s monitoring spotted the attacks, and some companies disconnected their sites from the internet and ran them locally until it was safe.
Based on the examples we have referenced so far, the layers failed where they weren’t really separate. In Ukraine in 2015, the VPN led straight into the control network. At the Polish wind farm, the network was divided into segments, but administrator rights on the one device that managed them gave the attacker an account that reached all of them.
Dragos describes the same problem with ransomware: attackers typically log into the VPN with stolen credentials, then encrypt the virtualisation hosts that run SCADA and historian servers, reaching OT “without touching a single industrial protocol”. When ransomware did reach OT in 2025, every case Dragos handled caused significant operational disruption.
What are the patterns that have worked
The key survival factor in each of these attacks has come down to one attribute - independence.
- Independent credentials Each layer needs its own accounts, held in its own store. If one device or directory shares access to every layer, there’s really only one layer.
- Independent vendors A single flaw shouldn’t open two doors. The corporate gateway and the OT access broker should come from different vendors, and so too for external firewalls.
- Independent infrastructure OT servers shouldn’t run on virtualisation platforms, backup systems or management tools that are administered from the corporate IT network.
- No secondary paths Backup cellular links, vendor modems and networks shared with the network operator need the same controls as the main path, or they become an attacker’s main path.
- Fail-safe operation Generation that keeps running safely without communications is the layer that held in Poland and Germany. Keep it that way, and test it.
- Continuous monitoring Layers rarely stop a determined attacker outright, but they can slow them down. Rapid detection lets operators isolate OT assets from the internet before damage is done.
What operators should do
Now, if you are lucky enough to be running NetScaler:
- Apply the fixed builds, then hunt for compromise back from early September 2026. Citrix has published IOCs in NetScaler Console.
- Reset sessions and credentials that have passed through the gateway over this period.
- Extend the hunt to jump hosts and OT login logs to trace any onwards movement.
Structurally, alongside the independence principles above:
- Two gates. The corporate gateway takes users only as far as an OT demilitarised zone. A second broker, owned by the OT team, controls everything beyond it.
- Multi-factor authentication on a separate channel. A phone push or hardware key makes a captured password useless on its own.
- Sessions, not tunnels. Remote users get a recorded session to a specific jump host or application, never a routed network connection into OT.
- Nothing listening on the internet where possible. Site connectors that only make outbound connections can’t be found by the internet-wide scanning this year’s campaigns rely on.
- Vendor access on request. OEM and contractor sessions are approved per session, time-limited and recorded, with no permanently connected vendor gateways.
None of this is new. ASD and its Five Eyes partners published guidance on securing edge devices in 2025, and IEC 62443 has described zones and conduits for years. The Australian Energy Sector Cyber Security Framework covers it under its Access and Architecture domains.
The key takeaway: watch the landing zone
Every example above follows the same path. The attacker gets through the front door, then has to keep moving: gateway to jump host, jump host to site, site to site. The OT DMZ where remote users land is the one place every attack must pass through, which makes it the best place to catch one.
An attacker with stolen credentials looks like a legitimate user. What gives them away is that nobody expected them. In a well-run system, every arrival in the landing zone is predictable: an engineer at the jump host matches an approved work order, for a named site, within an approved window. Anyone else raises an alarm within minutes.
Few operators achieve this. Work orders are raised after the work starts, windows slip, engineers log in at 2am to deal with faults, and OEMs connect on their own schedule. The security team holds the remote access logs, the OT team holds the change calendar, and the two are usually compared only after an attacker has been found inside the OT environment.
Closing this gap should be a standing duty for security operations:
- No session without a work order. Every session into the landing zone carries a change reference. Sessions without one raise an alarm.
- Reconcile daily. Exceptions go back to the OT asset owner to explain. Emergency access is allowed, but logged as break-glass and reviewed.
- Time-bound privileges. Vendor sessions are held to the scope requested, and access is removed when the window closes.
If real-time alarms aren’t practical yet, start with the daily reconciliation. It’s cheap, it shows how well change management really works, and in Australia it’s the evidence the enhanced SOCI rules will expect from June 2027.
The Polish attacker spent more than a week scanning before reaching the heat and power plant. The next critical alert is a matter of when, not if. What decides the outcome is whether anyone notices the intruder in the landing zone before they move deeper.