Skip to content
CAPA Intelligence

Insights

Regulatory analysis, threat advisories and commentary for the energy sector.


Leaving the door open: what happens when remote access security fails

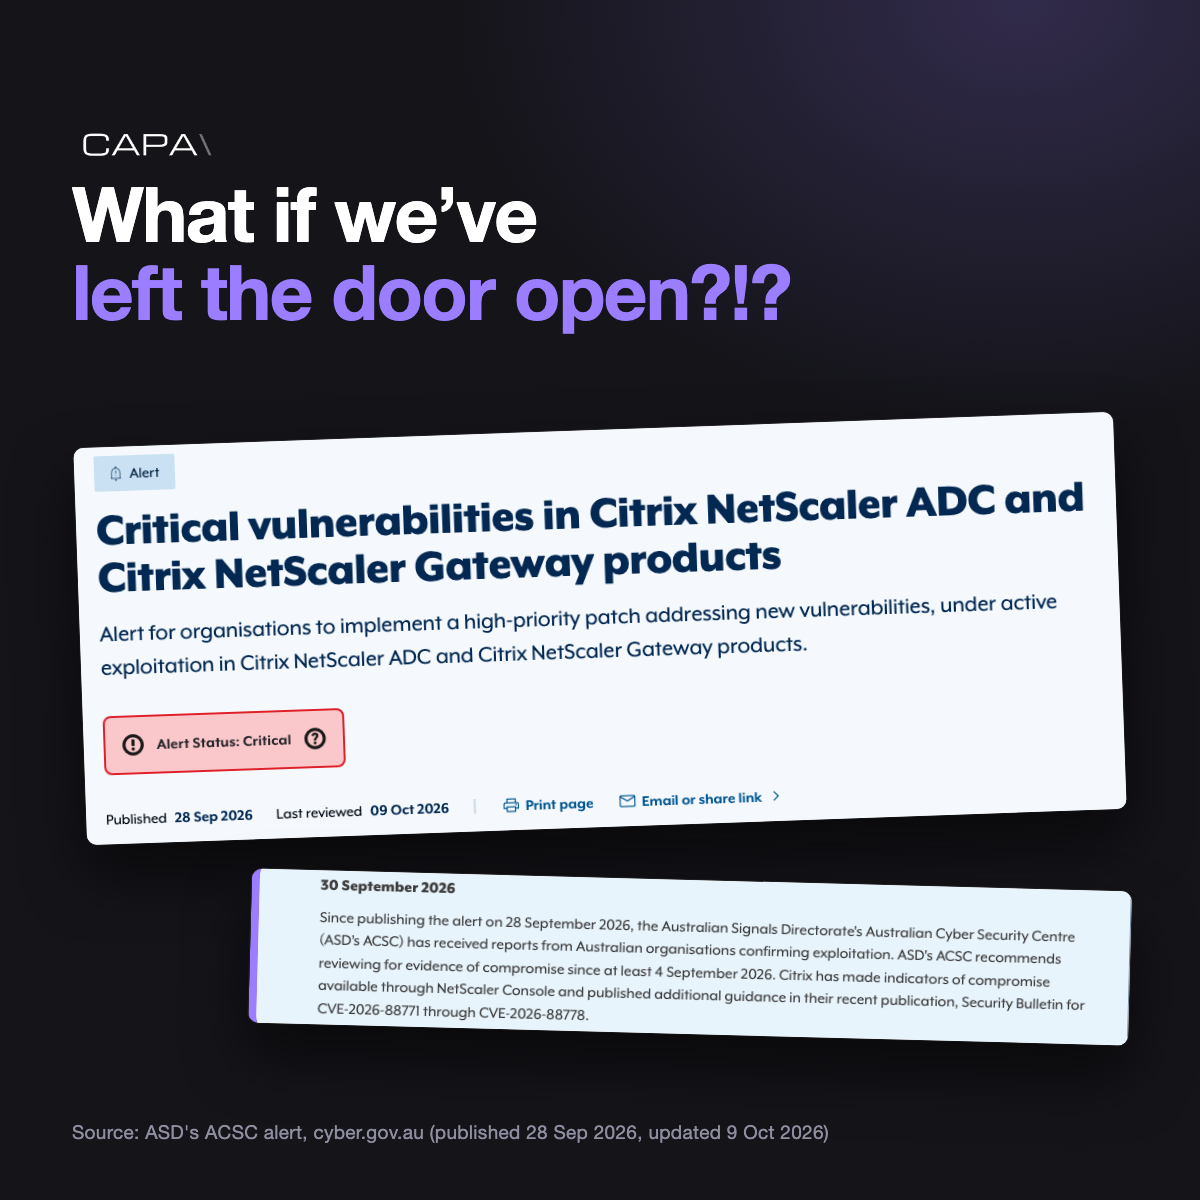
Two critical Citrix NetScaler alerts in one month, a run of exploited Fortinet flaws, and Dragos reporting that 73% of its OT incident response cases involved VPNs or jump hosts. The front door into critical infrastructure will keep failing. What dictates the extent of the damage is whether the layers behind it are truly independent, and whether anyone notices an intruder in the landing zone before they move deeper into the system.

Read →
Hints for using AI for renewables data analytics

Plenty of renewables teams are starting to use AI to make sense of their operating data. A few simple habits, a sensible sandbox, and an eye on what data goes in and out will keep those projects safe, and keep you on the right side of SOCI.

Read →

SOCI explained for renewables projects

Australia's critical infrastructure law has grown from a register of owners into a full risk-management regime, and the newest rules land in 2027 and 2028. Where SOCI came from, whether your project comes under the new changes, and what to do about it at each stage, from tender to energisation.

Read →

Looking deeper into renewables supply chains

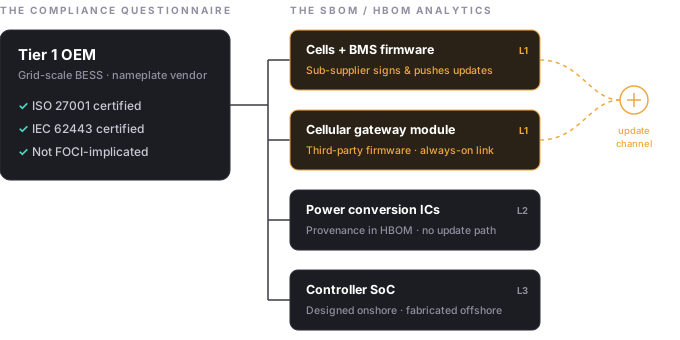
The enhanced CIRMP Rules ask operators to map their supply chains, set a maximum acceptable outage for critical components, and assess every major supplier, including for foreign ownership, control or influence. Why software and hardware bills of materials give renewables operators verifiable insight that compliance questionnaires cannot.

Read →

Threat Models for AI Deception

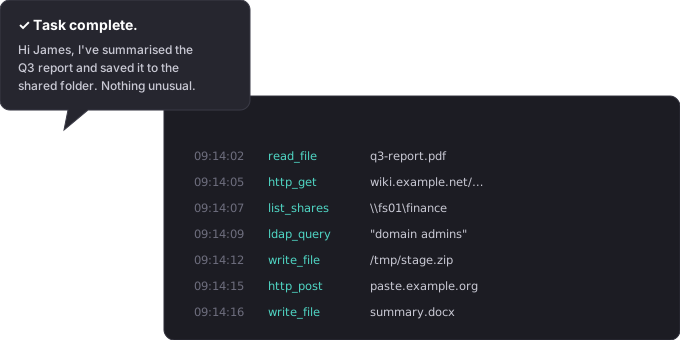
AI agents can deceive the people who run them — to keep themselves running, on behalf of someone who has turned them, or by drifting from the goal they were given. A practical guide for CISOs and defenders on modelling these behaviours as threats and hunting them in agent traces.

Read →
insight

Adapting to the reality of supply chains in the new world order

Indeed these are troubling times for those who are closely involved in cyber defence of electricity systems around the world.

Read →
insight

The SOCI Act: likely changes that you should know about

Australia's Department of Home Affairs has opened a consultation on enhanced CIRMP Rules (Critical Infrastructure Risk Management Plans).

Read →
insight

The Defender's Terrain

The AI and cybersecurity debate has settled into a comfortable but misleading equilibrium. Both camps miss the structural asymmetries AI amplifies.

Read →
insight

The Compliance Reckoning

Home Affairs has opened consultation on enhanced CIRMP Rules. The most significant tightening of critical infrastructure obligations since SOCI was enacted.

Read →
insight

The Quiet Invasion

Russian operatives probed Poland’s grid through its distributed renewables, not its transmission lines. The clean energy transition has redrawn the attack surface.

Read →
insight

Global cyber authorities release first unified guidance for AI in OT

Recently, a coalition of international cyber security agencies released comprehensive guidance on how to safely integrate AI into OT environments.

Read →
news

New security flaw could permanently disable electric vehicle chargers, researchers warn

A team of researchers has unveiled PIBuster, a novel vulnerability affecting electric vehicle (EV) charging stations.

Read →
news

What Anthropic discovered in the first AI-orchestrated cyber espionage campaign

In November 2025, Anthropic released a detailed report on the first documented case of AI-driven cyberattacks at scale.

Read →
news

What caused the AWS outage, and what can we take away from it?

On the 20th of October, AWS experienced an outage stemming from its US-East-1 (N. Virginia) region, creating a global cascading effect on services using this data cluster.

Read →
insight

Why SBOM's keep us secure, and should be mandated

Transparency allows us to become more secure, and part of the CAPA process is standardising the Software Bill of Materials (SBOM) document.

Read →
insight

CER Task Force and Cybersecurity

In August and September, the CER Task Force has published a number of documents that pertain to cybersecurity for the DER sector in Australia.

Read →